 FF2K · The Bunker Desk · October 3, 2026
Bitcoin is protected by huge numbers, good randomness, and the modest hope that nobody turns sound cryptography into community theater.
Yeti Cold Storage starts with a serious idea: make seven keys, distribute them geographically, and require any three to spend. Lose four backups and you can still recover. An attacker needs three. Bitcoin Core does the cryptographic work.
That is not nonsense. Three-of-seven multisig is real security engineering.
The problem starts when a tradeoff becomes a tribe.
For years, a small group of overlapping Bitcoin personalities promoted Yeti alongside #GetOnZero—the campaign to hold little or no fiat and convert back only when needed. The pitch arrived with the usual social accessories: podcasts, slogans, ridicule of alternatives, and the suggestion that hesitation meant cowardice or stupidity.
The blockchain is less emotional. It just keeps receipts.
The math worked. The ritual talked.
Alex Thorn supplied the author with an on-chain report and said he used Google BigQuery to identify candidate transactions, then verified them against his local full node. The report covers legacy Yeti activity through block 969,680.
It identified:
836 legacy Yeti-template spending transactions;
1,055 revealed addresses;
1,461.41 BTC in gross input value; and
359 test-sized transactions below 0.001 BTC—43% of the total.
Those numbers are useful. The signer data is the real story.
Legacy Yeti used native SegWit P2WSH with seven keys kept in seed order. Its guide told users to make small test spends with particular backup combinations: first keys 1-2-3, then 4-5-6.
There are 35 possible three-key combinations. Random selection would put each near 2.9%.
The report rebuilt each input’s SegWit signature hash and matched the three signatures to their positions in the seven-key script. Keys 1-2-3 appeared in 20.8% of legacy Yeti-template inputs. Keys 4-5-6 appeared in 9.5%.
This was not a one-trait guessing game. The study checked every revealed script against its spent address, verified every signer match, and reran the signature test with each input amount altered by one satoshi; the false version matched nothing. It also recovered a mainnet transaction from Yeti’s published developer-test history as a positive control and found no qualifying pure three-of-seven P2WSH spend before that October 2019 test. None of those controls proves the software used in every individual transaction. Together, however, they make “legacy Yeti-template” considerably more than chain-analysis astrology.
FF2K independently repeated three sample checks against public transaction data. We parsed each witness, confirmed the script hash matched the spent P2WSH output, and independently performed the BIP143/ECDSA signature checks. The published positive control at transaction 01e31e…bc13 was unsorted three-of-seven signed by positions 1-2-3. The first classified template spend, 743485…dc0b, was unsorted three-of-seven signed by 5-6-7. A post-guide example, b75a5e…15e9, was unsorted three-of-seven signed by 4-5-6. All three matched the report exactly.
Then came the cleaner test. Before Yeti added the 4-5-6 instruction in January 2021, that combination appeared 3.0% of the time—almost exactly chance. After the instruction appeared, it jumped to 14.8%.
The wallet never printed “Made with Yeti” on-chain. It did something more revealing: it trained users to perform the same public ceremony.
Seven keys. Seven envelopes. One very chatty checklist.
What a spend actually reveals
Before a Yeti output is spent, the chain shows a P2WSH script hash. It does not reveal “Yeti,” the threshold, the seven public keys, or the parent xpubs.
Spending changes that. BIP141 requires the full witness script to appear in the transaction witness. A legacy Yeti spend therefore reveals:
the three-of-seven policy;
all seven derived public keys for that address;
three valid signatures;
which three key positions signed; and
the transaction graph around the spent coins.
It does not reveal private keys. It does not reveal the seven parent xpubs. And it does not automatically expose every address in the wallet.
So “Yeti destroys privacy” is satisfying copy but sloppy analysis. The accurate criticism is better:
A legacy Yeti spend leaves a permanent, unusual fingerprint. Address reuse, consolidation, funding history, timing, change detection, or descriptor leakage can turn that fingerprint into a wider wallet cluster.
Legacy Yeti’s own documentation admitted that uncommon three-of-seven spends could lead observers to infer Yeti usage. A Yeti 2.0 issue later described the smaller anonymity set and recognizable fingerprint directly.
The current threat model also admits that one stolen backup disc can reveal the watch-only descriptor—a “balance oracle” that cannot steal the bitcoin but can expose the owner’s financial history.
The coins may be safe. Your business may not be.
Forty-three percent testing
Testing backups is smart. A recovery plan never rehearsed is just fan fiction stored in envelopes.
Broadcasting every rehearsal is a separate decision.
A local recovery check reveals nothing on-chain. An offline PSBT that is never transmitted reveals nothing on-chain either, although PSBT files can contain sensitive wallet metadata. Broadcasting the test permanently publishes the script and signing pattern of every spent input.
That still does not expose the whole vault by magic. Wider damage requires address reuse, consolidation, recognizable change, connected funding, or a leaked descriptor. But Yeti repeatedly chooses a public proof where a private recovery check could answer the narrower question.
The cryptography kept the secret. The operating procedure kept volunteering clues.
Adoption, or one whale wearing 35 coats?
The report found that 40 spends of at least 10 BTC carried 1,099.49 of the 1,461.41 measured BTC.
One heuristic owner cluster accounted for roughly 1,050.82 BTC—72% of the total. In December 2024, 35 transactions moved 860.31 BTC within about an hour from separately funded legacy-Yeti addresses into fresh P2WSH outputs. Seven destinations later spent and revealed the same template. The other 28 remained unspent at the cutoff and held 700.31 BTC.
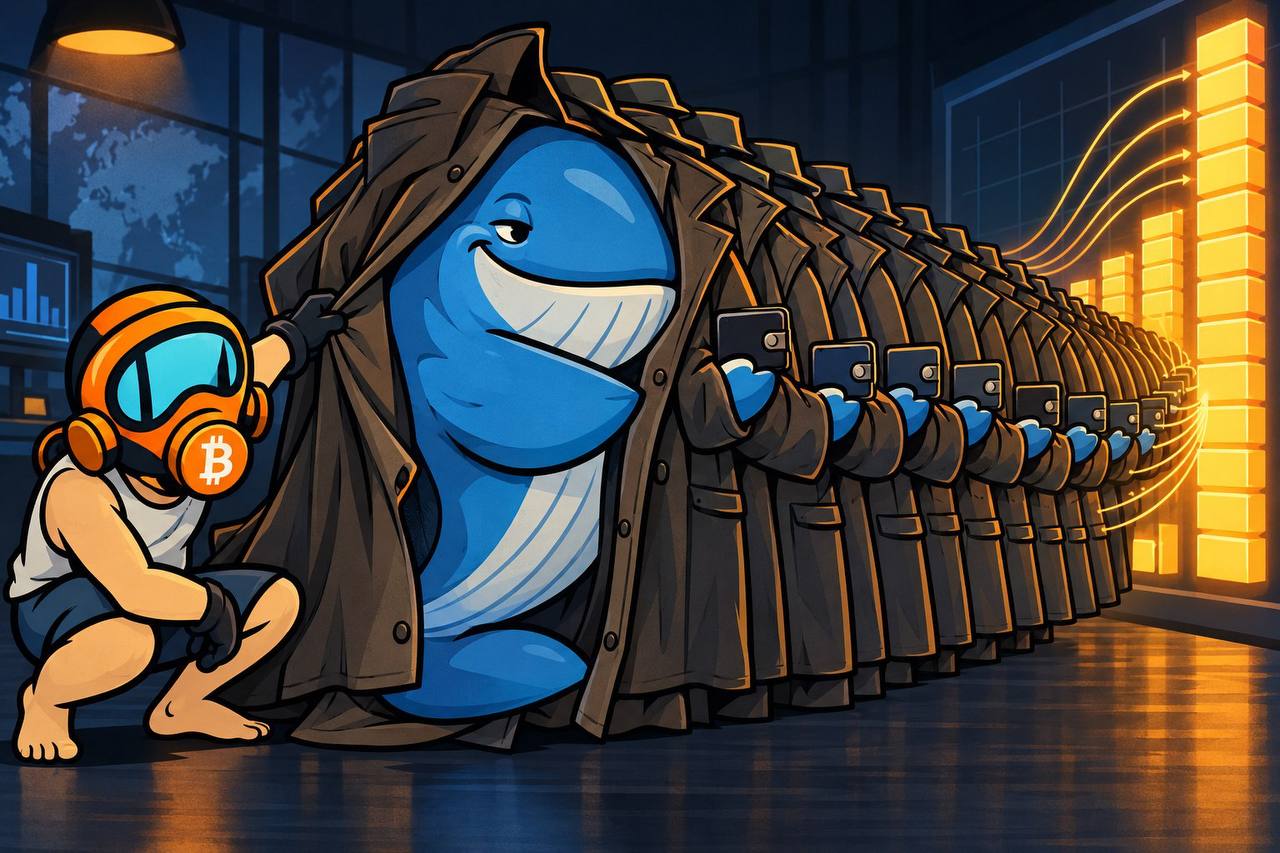
That looks like one owner rotating into a fresh Yeti setup. It is not proof until those scripts move.
This matters because aggregate volume can resemble mass adoption when one owner supplied most of it. The report estimates roughly 469 owners after adding timing and funding heuristics, but 317 revealed only one address.
The measured 13.35 BTC still sitting on already revealed legacy-Yeti addresses is also not total Yeti holdings. Unspent scripts remain hidden. The number is a floor, not a balance sheet.
Apparently even blockchains need footnotes. Marketing departments remain devastated.
Not every 3-of-7 is Yeti
The report separately found 1,112 BIP67-sorted three-of-seven transactions moving 85,997.10 BTC—nearly 59 times the legacy-Yeti total.
A three-of-seven script is not proof of Yeti. Even an unsorted legacy-style script is probabilistic attribution, not a software serial number. The report’s case rests on the combined fingerprint: unsorted seed-order keys, known transaction shapes, full-balance sweeps, the guide’s favored signer combinations, and a positive-control transaction from Yeti’s published testing history.
There is also a version boundary. Yeti 2.0 now prescribes wsh(sortedmulti(3,...)), unlike legacy Yeti’s unsorted multi() construction. The report measures the legacy template. Sorted three-of-seven transactions after Yeti 2.0’s August 2026 launch cannot automatically be labeled “not Yeti.”
If we are criticizing fingerprints, we should avoid manufacturing one with lazy attribution.
Seven locations—until spending day
Yeti’s geographic redundancy is a legitimate strength. Seven distributed backups improve survivability against loss and single-location theft.
Then the normal spending procedure gathers three backups and loads them into one offline computer session.
That laptop becomes a temporary quorum.
Air-gapping reduces remote exposure. It does not repeal compromised firmware, hostile removable media, destination substitution, supply-chain risk, or operator error. Bitcoin Core and PSBT provide sound building blocks. The question is why three independently stored keys must become simultaneously available to one general-purpose endpoint.
Yeti 2.0’s FAQ acknowledges that one-key-per-session signing would prevent a quorum from existing on one signer, but treats the added sessions as complexity.
Fair enough. Complexity is a cost. So is concentrating three keys on one machine. That is called a tradeoff—not a heresy.
Taproot is not a magic word either
Yeti 2.0 still recommends native P2WSH sortedmulti, not Taproot. A September 2026 tapscript/FROST proposal closed without implementation.
A Taproot script-path multi_a(3-of-7) would hide the policy until spending, but the executed script would still be revealed. It would not look like an ordinary single-key payment.
A threshold Schnorr or FROST-style key-path design could make a cooperative three-of-seven spend look like a normal Taproot signature. It also introduces interactive signing, nonce management, distributed key-generation questions, and harder recovery.
The honest comparison is not “old idiots versus new Taproot.” It is mature but distinctive P2WSH versus more private but operationally harder threshold signing. Yeti chose the former. Users deserve to hear the tradeoff without the tribal soundtrack.
From Get On Zero to chatbot warfare
The Yeti promoter network overlaps with #GetOnZero through figures including JW Weatherman, Heavily Armed Clown, and Rollo McFloogle. In a 2022 interview, HAC said Get On Zero was not a purity test and conceded that “minimize fiat” might have been more precise—but the confrontational slogan generated discussion.
That pattern matters: reduce a risk decision to a moral binary, collect attention from the fight, then soften the literal claim under scrutiny.
During the 2026 Coldcard controversy, JW described the incident as an “inside job” with certainty far beyond anything our research verifies. Other posts aimed “scammers,” “shady,” and similar language at named professionals and companies. Those posts prove the rhetoric happened. They do not prove the accusations.
HAC later described adding THREAT_MODEL.md, CONTEXT_FOR_ADVISORS.md, and llms.txt to Yeti 2.0, then testing prompts until Grok became more favorable. He called it a “nuclear weapon in information warfare” and celebrated using agents to rebut critics at scale.
He disclosed the method himself. No conspiracy theory needed.
Call it documentation, robot SEO, or deliberate LLM context engineering. But there is exquisite comedy in watching “don’t trust, verify” become “rewrite the context until the chatbot agrees.”
The actual lesson
Yeti is not fake cryptography. It is a bundle of choices:
redundancy over simplicity;
distributed backups but temporary quorum colocation;
wide descriptor availability but weaker financial privacy;
broadcast tests instead of strictly local recovery checks;
mature P2WSH instead of harder threshold-signing privacy; and
a distinctive procedure promoted by a loud social network.
Some users may rationally accept every one of those choices. What they should not do is adopt them because a few persistent accounts turned a threat model into a schoolyard loyalty test.
A hashtag is not a threat model. A podcast is not peer review. Bitcoin does not care who won the Space.
It only records what you revealed.
- FF2K